Clara Shinta
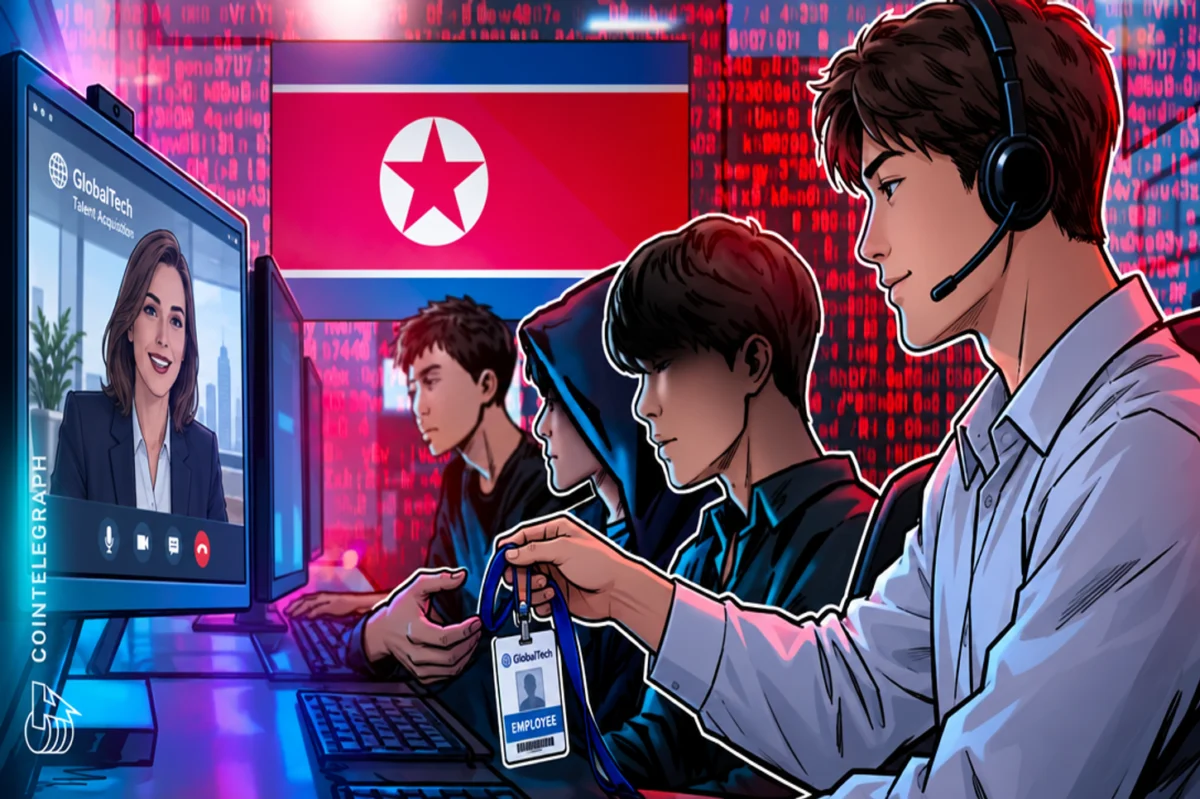
North Korea (DPRK) has significantly escalated its sophisticated cyber operations, now leveraging remote workers from third countries, including Iran and Lebanon, to infiltrate US companies. This elaborate scheme aims to illicitly acquire funds to finance the regime’s prohibited weapons programs, a development highlighted in a recent NBC report published on Friday, September 12, 2026. The strategy involves recruiting foreign IT professionals to successfully navigate stringent job interview processes, after which these positions are typically taken over by North Korean operatives who then exploit their access for espionage, data theft, and financial gain.
This revelation follows a comprehensive alert issued in July 2026 by the US government, in collaboration with several international agencies. The advisory specifically warned that North Korean IT workers "seek out contracts with the intent of remitting their salaries to their parent North Korean agencies. They also pose an insider threat to companies and are involved in data exfiltration, cryptocurrency theft, and theft of sensitive information." This underscores the multifaceted nature of the threat, moving beyond traditional cyberattacks to encompass human-element exploitation within corporate structures. As global governments intensify efforts to counter Pyongyang’s illicit activities, the DPRK has increasingly refined its tactics, turning to this indirect recruitment method to circumvent detection and access valuable targets. The NBC report detailed instances where foreign IT workers were scouted on professional networking platforms like LinkedIn, with some reportedly offered monthly payments of $500 in cryptocurrency to act as "interview associates," facilitating the initial breach.
The Modus Operandi: A Sophisticated Deception
The intricate nature of North Korea’s latest cyber infiltration strategy marks a significant evolution in its state-sponsored illicit activities. Unlike direct hacking attempts that might be traced back to DPRK IP addresses or known attack vectors, this method relies on a sophisticated social engineering and identity deception framework. The initial phase involves identifying and recruiting legitimate, often unsuspecting, IT professionals from countries like Iran and Lebanon. These individuals, potentially attracted by seemingly legitimate remote work opportunities and cryptocurrency payments, are tasked with passing rigorous job interviews for positions within US companies. Their genuine skills and clean digital footprints allow them to clear initial hurdles, background checks, and technical assessments that North Korean operatives might otherwise fail.
Once a contract is secured, the North Korean operatives systematically take over the remote work accounts. This handover can occur through various means: the recruited individual might unknowingly provide login credentials, or the North Koreans might establish remote access through malware disguised as legitimate software updates or tools. The use of virtual private networks (VPNs) and proxy servers further obscures the true origin of the operatives, making it appear as though the legitimate third-country worker is still performing the job. This deception allows North Korean agents to gain privileged access to corporate networks, intellectual property, and financial systems, often operating undetected for extended periods. The financial transactions, including the payments to the "interview associates" and the subsequent siphoning of funds, are frequently conducted using cryptocurrencies, which offer a degree of anonymity and make tracing difficult for traditional financial institutions.
Official Warnings and the Growing Threat Landscape
The July 2026 alert, issued by agencies such as the Federal Bureau of Investigation (FBI), the Cybersecurity and Infrastructure Security Agency (CISA), and the Department of the Treasury, represents a critical response to this evolving threat. These agencies routinely monitor and report on North Korean cyber activities, emphasizing the severe risks posed to national security and economic stability. The alert specifically highlighted the "insider threat" aspect, a particularly insidious form of cyber espionage where malicious actors gain legitimate access to an organization’s systems, making detection and mitigation significantly more challenging than external attacks. The warning enumerated specific malicious activities undertaken by these operatives, including data exfiltration—the unauthorized transfer of data from a computer or network—theft of sensitive information, and extensive cryptocurrency theft.
The US government’s persistent warnings underscore the scale and persistence of North Korea’s cyber efforts. These advisories are not isolated incidents but rather part of a broader, ongoing campaign to inform and protect US entities from state-sponsored threats. The inclusion of foreign agencies in the joint alert also signals the international dimension of this problem, indicating that North Korea’s recruitment efforts and operational reach extend beyond specific geographical boundaries, leveraging global talent pools and remote work trends.
The Financial Imperative: Funding WMD Programs
At the core of North Korea’s aggressive cyber strategy is a desperate need for foreign currency to circumvent crippling international sanctions and finance its illicit weapons of mass destruction (WMD) programs. Decades of UN Security Council resolutions and unilateral sanctions from countries like the United States, Japan, and South Korea have severely restricted Pyongyang’s access to conventional international finance, trade, and resources. Consequently, the regime has increasingly turned to illicit means, with cybercrime emerging as its most lucrative revenue stream.
The funds acquired through these sophisticated IT worker schemes, along with direct cryptocurrency hacks and other cyber-enabled financial crimes, are directly channeled into the development of nuclear weapons, ballistic missiles, and other advanced military capabilities. This direct link between cyber theft and WMD proliferation presents a grave national security threat, making the disruption of these financial networks a top priority for intelligence agencies worldwide. Each successful infiltration or cryptocurrency heist strengthens Pyongyang’s ability to defy international norms and escalate regional tensions.
Escalation of Cyber Operations: A Historical Perspective
North Korea’s foray into cyber warfare is not a recent phenomenon but rather the culmination of decades of strategic investment in its cyber capabilities. Early instances of DPRK cyber activity, often attributed to groups like the notorious Lazarus Group (also known as APT38 or Hidden Cobra), date back to the early 2000s. Initially, these attacks focused on South Korean government and financial institutions, primarily for disruption and espionage.
A significant turning point came with the 2014 Sony Pictures Entertainment hack, which garnered international headlines and demonstrated North Korea’s willingness to engage in highly disruptive cyberattacks for political motives. This event marked a shift in global perception regarding North Korea’s cyber prowess. Following this, and particularly after the intensification of international sanctions, North Korea’s cyber units pivoted heavily towards financial institutions and, critically, cryptocurrency platforms. The global emergence of cryptocurrencies offered a relatively unregulated and decentralized financial ecosystem, perfectly suited for sanctions evasion and large-scale theft without traditional banking intermediaries. Groups like Lazarus, Kimsuky, and Andariel have since been implicated in numerous high-profile cryptocurrency exchange hacks, bank heists, and ransomware campaigns, collectively siphoning billions of dollars. The current tactic of exploiting third-country IT workers represents a further evolution, showcasing the regime’s adaptability and determination to overcome countermeasures.
The Cryptocurrency Connection: A Double-Edged Sword
Cryptocurrency plays a dual role in North Korea’s illicit operations: it is both a primary target for theft and a preferred medium for payments and money laundering. Cybersecurity firm CrowdStrike reported in May 2026 that North Korean state-affiliated hackers were responsible for over $2 billion in crypto losses in 2025 alone, marking a staggering 51% year-on-year increase. This figure underscores the immense profitability of these operations and the significant resources North Korea is dedicating to them. These funds are laundered through complex chains of transactions, mixers, and decentralized exchanges to obscure their origins before being converted into fiat currency or used to purchase sanctioned goods.
Furthermore, cryptocurrency is explicitly used to facilitate the recruitment and payment of the "interview associates." The promise of monthly payments in digital assets like Bitcoin or Ethereum, often advertised as part-time or flexible work, can be particularly appealing in regions facing economic hardship or where access to traditional banking services might be limited. This method not only provides a discreet payment channel but also adds another layer of obfuscation to the entire scheme, making it harder for financial regulators to track the flow of funds from the initial recruitment to the ultimate beneficiaries in Pyongyang. The pseudo-anonymity and borderless nature of cryptocurrencies make them an ideal tool for a regime operating under severe financial restrictions.
Case Studies and Reported Incidents
While the NBC report highlighted the general trend, previous incidents have provided concrete examples of North Korea’s infiltration attempts. In an earlier related incident, Cointelegraph reported that the blockchain software technology company Consensys unknowingly outsourced developer work to a North Korean individual. Although the full extent of compromise in that specific case was not publicly detailed, it served as a stark reminder of the vulnerability of global remote work models and the sophisticated methods employed by North Korean agents to embed themselves within legitimate tech ecosystems. Such incidents demonstrate that even well-resourced technology companies are susceptible to these infiltration tactics, which often exploit trust, remote access protocols, and the sheer volume of global freelance talent.
The Global Impact and Vulnerabilities
The implications of North Korea’s evolving cyber tactics extend far beyond the immediate financial losses. For US companies, particularly those in critical sectors like defense, finance, and technology, the infiltration by North Korean operatives poses significant risks:
- Intellectual Property Theft: Access to proprietary technologies, research and development data, and trade secrets can severely undermine a company’s competitive edge and national economic security.
- Supply Chain Compromise: If an infiltrated company is part of a larger supply chain, the compromise could ripple through multiple organizations, creating systemic vulnerabilities.
- National Security Risks: Espionage activities targeting government contractors or critical infrastructure companies could provide Pyongyang with sensitive intelligence, jeopardizing national defense.
- Reputational Damage: Companies discovered to have been infiltrated face severe reputational damage, loss of customer trust, and potential legal liabilities.
- Financial Disruption: Beyond direct theft, the costs associated with remediation, enhanced cybersecurity measures, and potential regulatory fines can be substantial.
The broader global implications include the continued funding of a rogue state’s WMD programs, undermining international non-proliferation efforts, and exacerbating geopolitical instability. The exploitation of remote work trends also exposes a significant vulnerability in the modern globalized workforce, where geographical boundaries are blurred, and digital identities can be easily manipulated.
Responses and Countermeasures
Governments and private sector entities are intensifying their efforts to combat this evolving threat. Key countermeasures include:
- Enhanced Due Diligence: Companies are advised to implement more rigorous background checks, identity verification, and continuous monitoring for remote employees and contractors, especially those working in sensitive roles or with access to critical data.
- Cybersecurity Awareness Training: Educating employees about social engineering tactics, phishing attempts, and the risks associated with suspicious recruitment offers is crucial.
- Multi-Factor Authentication (MFA) and Least Privilege Access: Implementing strong access controls, including MFA, and ensuring employees only have access to the information and systems absolutely necessary for their job functions can limit the damage of a breach.
- Threat Intelligence Sharing: Collaborative efforts between government agencies, cybersecurity firms, and private companies to share threat intelligence and indicators of compromise (IOCs) are vital for proactive defense.
- International Cooperation: Strengthened international cooperation to track and disrupt North Korean cyber networks, seize illicit funds, and impose sanctions on facilitators is essential.
- Blockchain Analytics: Companies specializing in blockchain analytics are increasingly vital in tracing stolen cryptocurrencies and identifying laundering pathways, aiding law enforcement in recovery efforts.
Expert Analysis and Future Outlook
Cybersecurity experts uniformly agree that North Korea’s cyber capabilities are continually advancing, demonstrating remarkable adaptability to counter global efforts to contain its illicit financing. Analysts from organizations like Mandiant and Chainalysis frequently publish reports detailing the sophistication of DPRK’s tactics and the significant financial impact of its operations. The shift towards exploiting legitimate IT worker roles signifies a move towards "living off the land" within target networks, making detection harder as the initial access appears legitimate.
The future outlook suggests that North Korea will continue to innovate its methods, exploring new technologies and vulnerabilities. The increasing adoption of decentralized finance (DeFi) and new blockchain technologies could present fresh avenues for exploitation. The global reliance on remote work, accelerated by recent global events, will likely remain a fertile ground for these types of infiltration schemes. Therefore, continuous vigilance, robust cybersecurity investments, and a proactive, collaborative approach are paramount to mitigating the persistent and evolving threat posed by North Korea’s state-sponsored cyber operations.
Economic Resilience Amidst Sanctions
Despite the crushing weight of international sanctions designed to cripple its economy, North Korea has shown a surprising degree of resilience, partly fueled by the success of its illicit cyber activities. The Bank of Korea, for instance, estimated that North Korea’s Gross Domestic Product (GDP) increased by 3.5% in 2025, a remarkable figure given the regime’s isolation. While this growth is likely driven by a combination of factors, including domestic resource exploitation and possibly some clandestine trade, the significant influx of funds from cybercrime undoubtedly plays a crucial role in shoring up the regime’s finances and sustaining its military-industrial complex. This economic resilience, directly linked to the success of its cyber operations, further motivates Pyongyang to invest in and expand its illicit cyber capabilities.
In conclusion, North Korea’s sophisticated strategy of leveraging third-country IT workers to infiltrate US companies represents a significant and escalating cyber threat. This method not only provides a stealthy pathway for espionage and data theft but also serves as a critical financial lifeline for the regime’s illicit WMD programs. As global governments and private sectors strive to counter these evolving tactics, the imperative for enhanced vigilance, robust cybersecurity measures, and international cooperation becomes ever more critical to safeguard national security and economic stability against a determined and adaptable adversary.
Cointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently.